Authenticator - 2FA & Password
FIRE Ltd
- 2.7
- 56.00 Reviews
- 1.00M
- Downloads
- Free
- Price
Screenshots
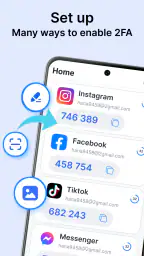
Authenticator - 2FA & Password Pros and Cons
Pros
- Supports secure two-factor authentication for multiple accounts.
- Generates time-based codes even without an internet connection.
- Can help organize passwords and authentication entries in one place.
- Adds an extra security layer beyond usernames and passwords.
- Useful for protecting email, social media, and work accounts.
Cons
- Losing the device may make account recovery difficult without backups.
- Some features may require a subscription or in-app purchases.
- Moving accounts to a new phone can require careful manual setup.
- Not every online service supports the same authentication methods.
- Password storage increases risk if the app or device is poorly secured.
 Analysis by All-app
I tried Authenticator - 2FA & Password as a practical security tool rather than treating it like another app to install and forget. Its purpose is straightforward: keep one-time verification codes available when a service asks for a second sign-in step, while also presenting itself as a password-related tool. That makes it relevant to anyone who is gradually moving away from relying on text messages for account protection.
My first impression is mixed. The app is easy to understand at a glance, and the basic idea is useful for everyday logins. At the same time, an authenticator is only as good as its setup, recovery habits, and reliability when you urgently need a code. I would therefore recommend approaching this app as part of a wider account-security routine, not as a magic shield. It can be convenient, but convenience should not replace careful backup planning.
How the app feels in current use
FIRE Ltd publishes this free tools app for Android users, with an Everyone content rating and support beginning with Android 9. It reached the store on August 9, 2024, and the current version is 72.0. Those details matter because an authenticator must fit comfortably into the phone you already use for work, banking, shopping, social accounts, or email. Compatibility with Android 9 and later gives it a reasonably broad audience without making it relevant only to very recent phones.
The store presence is substantial, with over one million installs, but the average rating is around 2.7 from roughly one thousand ratings. I would not ignore that signal. A security app can receive poor reactions for many reasons, including setup confusion, lost access after changing phones, or expectations that are not explained clearly enough. Still, a low average rating tells me to test the workflow carefully before moving every important account into it.
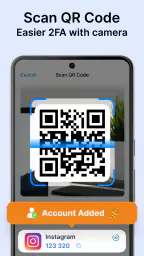
The central use case is familiar. When a website or service offers an authenticator-app option, it normally shows a setup key or a QR code. You add that account to the app, then use the changing code during sign-in. The important practical point is that the code is usually time-sensitive. If the phone clock is significantly wrong, a correct-looking code may fail. I always check automatic date and time before blaming the app or the account provider.
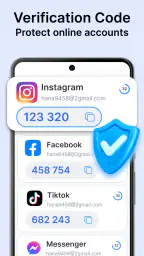
For a normal day, the benefit is simple: I can open the tool, find the relevant account, and copy or read the current verification code instead of waiting for a message. That is especially useful when mobile reception is poor, when I am travelling, or when I want to avoid making text messages the only second factor. It also keeps the authentication step close to the device I already carry.
A realistic account setup routine
If I were setting this up for an email account, I would not begin by deleting the existing recovery methods. I would first enable two-factor authentication on the email provider, choose the authenticator option, and keep the provider’s recovery codes somewhere safe. Only after testing a fresh sign-in would I consider reducing reliance on less secure or less convenient methods.
More Reads From Our News Desk

Switching to the Xbox App: What Changes in Your Gaming Routine

Coloring & Learn Review: A Satisfying Canvas, Cluttered Menus

Microsoft 365 Copilot on Your Phone: Who Actually Needs It?

Mafia City: The Crime Saga That Outshines Its Rivals

Woodturning Transformed: How OS Updates Enhance Your Craft

How Tiles Hop EDM Rush Redefines Music Gaming
During setup, I would add one account at a time and label each entry clearly. A vague label such as “account” becomes a problem when several services are listed together. A name that identifies both the service and, where needed, the account address makes hurried sign-ins much less stressful. This is a small organizational habit, but it is one of the most useful ways to prevent choosing the wrong code.
My second check would be deliberate rather than automatic: I would lock the phone, reopen the app, and confirm that the code remains accessible when the login screen is waiting. I would also test the code before signing out of the service on another device. That catches mistakes in the setup key while I still have an active session available to repair them.
The most important preparation is a recovery plan made before the first phone problem. If the phone is lost, reset, or replaced, an authenticator may not be enough by itself to restore access. I would keep the account provider’s recovery codes offline and confirm that at least one legitimate recovery route works. This is not a criticism unique to FIRE Ltd; it is a basic trade-off of app-based verification that many people discover too late.
What the current version means for existing users
Version 72.0 is the current release, so existing users should make sure they are using that version before judging the present experience. An updated build can change screens, fix a setup issue, or alter how an account list behaves, but I would not assume that an update automatically solves account recovery. Updates improve the application; they do not replace the recovery arrangements controlled by each website.
For someone already using an earlier build, I would update at a calm moment rather than immediately before an important login. After the update, I would open several stored entries and verify that the labels and codes still appear as expected. This is a sensible habit for any security utility because the cost of a quick check is low compared with being locked out during a deadline.
New users should also understand the difference between an app update and a change to an authentication account. Updating the application is one thing; moving an account to a new phone is another. The second process depends on how the individual service handles authenticator enrollment. Some services provide a transfer route, while others require the old code, a recovery code, or a fresh setup process. I would never wipe the old phone until the new device has successfully completed a real sign-in.
The app’s free entry point makes it easy to try without committing money at installation. However, in-app purchases range from around five dollars to around sixty dollars per item. That is a wide range, and it makes me cautious about assuming that every useful part of the experience is included at no cost. Before confirming any purchase, I would read the exact screen carefully and decide whether the paid function is genuinely necessary for my workflow.
Where it is more useful than familiar alternatives
The usual alternative is text-message verification. An authenticator can be preferable when messages arrive slowly, when a phone number is being changed, or when I want the second factor to work without depending on the cellular network. It also avoids placing every login code in the same messaging inbox that may be visible through other devices or account-sync features.
Another alternative is a browser-based password manager with built-in one-time codes. That approach can be more efficient for people who want usernames, passwords, and verification codes filled in together. I would choose that kind of system when I manage many accounts and already trust its cross-device workflow. A separate authenticator can be a better fit when I want the verification step kept apart from the password store, reducing the chance that one compromised vault exposes both pieces of a login.
Hardware security keys are another important comparison. They can provide strong protection against phishing because the physical device participates in the sign-in, but they cost money and can be inconvenient if a spare is not available. This app is easier to start with and more portable in the everyday sense, yet it still depends on protecting the phone and preparing for its loss. For high-value accounts, I would consider an authenticator one layer rather than the only layer.
There is also a privacy trade-off in choosing a standalone tool. Keeping codes in a separate app may feel cleaner than placing them inside a broader password system, but separation can increase the number of places I must maintain. If I forget where a code is stored, or if I fail to document recovery steps, the extra separation becomes friction instead of protection. The best choice depends on whether I value compartmentalization more than one unified sign-in workflow.
Small workflow decisions that make a big difference
One useful habit is to keep the authenticator app out of the same rushed sequence as password entry. I prefer entering the password first, opening the code tool only when the service asks for the second factor, and then returning to the sign-in screen. This reduces the chance of copying an expired code and gives me a clear moment to check which account entry I am using.
A second habit is to avoid experimenting with account removal. If an entry looks duplicated or incorrectly named, I would first confirm which one works by starting a controlled sign-in. Removing an entry can be harmless if the setup secret is still available, but it can be troublesome if the original enrollment details are gone. Renaming or documenting an entry is safer than deleting it impulsively.
A third practical insight concerns phone replacement. I would treat migration as a project with a checklist: confirm recovery codes, identify every service using the old authenticator, enroll the new device, test each login, and only then retire the old setup. Doing this gradually is slower than transferring everything in one burst, but it limits the damage if one service needs a different recovery method.
I would also keep the phone itself protected with a strong screen lock and current system security updates. The authenticator cannot compensate for an unlocked device. A person who gains direct access to the phone may not need to defeat the account’s second factor in the usual way. This is an obvious point technically, but it is easy to overlook because the app feels like a separate security layer.
Where the experience still needs caution
The low average rating is the clearest reason I would recommend a measured trial instead of an immediate full migration. I want an authenticator to be predictable under pressure, and a rating around 2.7 suggests that some users have encountered enough friction to affect their overall experience. Ratings do not explain each individual problem, so I would test the app with a less critical account first and observe how comfortably I can add, find, and use an entry.
The password wording also deserves careful interpretation. I would not assume that a tool described with password-related language is a complete replacement for a dedicated password manager. Password storage, password generation, secure sharing, autofill, encrypted synchronization, and recovery are separate capabilities. Unless I can see and test a specific function in the app, I would continue using the password system I already trust rather than moving sensitive credentials based only on the name or summary.
Another gap is the human side of recovery. An authenticator can generate a code during a normal login, but that does not guarantee an easy path after a lost phone, a factory reset, or a broken screen. The correct response is not to keep every account permanently signed in. It is to prepare recovery codes and understand each provider’s recovery process while access is still available.
There is also a usability cost when the phone is the only place where the second factor lives. If I am signing in on that same phone, switching between the service and the authenticator can be awkward. A tablet, computer, or second device may make the process easier, but I would avoid casually creating extra copies of sensitive setup information. Convenience should be balanced against the number of devices that would need protection.
Who should use it, and who should skip it
I think this app is most suitable for someone who wants a dedicated place for one-time codes and is willing to handle recovery responsibly. It can be a sensible first step for a person moving away from text messages, especially if that person uses Android 9 or newer and prefers a separate tool rather than a full password-management suite.
It may also suit a user who has only a handful of accounts and wants a focused interface instead of a large collection of password features. In that situation, clear labels and a simple routine can matter more than advanced automation. I would still begin with a low-risk account, test the sign-in, and keep the provider’s emergency codes outside the phone.
I would skip it, or at least compare alternatives first, if I need dependable cross-device synchronization, a mature password vault, or seamless autofill across many services. I would also hesitate if I am not comfortable maintaining recovery records. For a business account, a family account, or anything tied to irreplaceable information, I would look closely at organizational controls and recovery options before relying on a standalone mobile authenticator.
People who frequently change phones should be especially careful. The app may be perfectly usable on the current handset, but the real test is whether the user has a documented way to move every account. If that process sounds confusing, a service with a clearly understood multi-device backup workflow may be a better match, even if it is less minimal.
What I would watch as the product evolves
Because the current build is 72.0, I would watch future updates for clearer onboarding, safer migration guidance, and transparent explanations of any password-related tools. Those are the areas that most affect confidence in a security utility. I would also pay attention to whether the app makes account organization and recovery planning easier without encouraging users to store everything in one place.
I would not judge future changes only by a new version number. For this kind of app, meaningful progress would be visible in the moments that matter: adding an account without confusion, recovering after a device change, finding the right code quickly, and understanding what a purchase actually provides. Those practical details matter more to me than a longer feature list.
My current recommendation is cautious but positive for the right user. Authenticator - 2FA & Password offers a straightforward route into app-based two-factor authentication, and its free availability makes a controlled trial easy. Yet I would not install it and immediately protect every important account. I would test one service, preserve recovery codes, verify the code during a real login, and only expand after the routine feels dependable.
In the end, I see it as a potentially useful security companion rather than a complete security strategy. It is strongest when I use it with careful labels, a protected phone, and a recovery plan prepared in advance. If those habits fit the way you manage accounts, it is worth trying. If you want an all-in-one password vault, automatic multi-device continuity, or the strongest phishing resistance available, another category of tool may serve you better.
Frequently Asked Questions
What is Authenticator - 2FA & Password used for?
Authenticator - 2FA & Password is designed to improve account security by generating time-based two-factor authentication codes and helping users manage login credentials. After adding a compatible online account, the app can produce verification codes required during sign-in. Its password-related tools may also help organize or protect credentials, depending on the features available in the current version.
How does two-factor authentication work in this app?
The app works with services that support standard authenticator-based two-factor authentication, usually through a QR code or a setup key provided in the account’s security settings. Once the account is added, the app generates a temporary code that changes regularly. You enter that code after your password when logging in, providing an additional layer of protection.
Can I use Authenticator - 2FA & Password without an internet connection?
In many cases, the app can generate time-based verification codes without an active internet connection because the codes are based on the device’s clock and a previously stored secret key. However, internet access may still be needed to download the app, synchronize or back up data, restore accounts, or use connected password-management features. Keeping the device time accurate is important.
What happens if I lose my phone or delete the application?
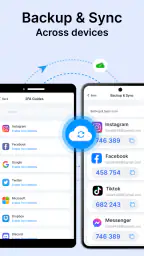
Losing your phone or removing the app can make it difficult to access accounts protected by two-factor authentication if no backup method is available. Before relying on the app, save each service’s recovery codes and check whether the application offers encrypted backup, export, or synchronization. You should also keep an alternative sign-in method, such as a trusted phone number or backup device.
Is Authenticator - 2FA & Password safe for storing passwords and authentication codes?
The app is intended to provide a more secure way to handle authentication codes and, where supported, passwords, but users should still review its privacy, backup, and lock-screen settings before storing sensitive information. Use a strong device passcode, enable biometric protection if available, keep the app updated, and avoid sharing screenshots or setup keys, since these can compromise your accounts.